Smart Password Manager TUI
A terminal user interface for smart password management built on smartpasslib
Generate deterministic passwords from secret phrases without storing them. No cloud, no database, no trust required.
smart-password-manager-tui-rs is a self-contained terminal application for managing smart passwords - passwords that are regenerated on demand from a secret phrase instead of being stored. It is built on top of the smartpasslib library and uses the same cryptographic algorithm as the Python, JavaScript, Kotlin, Go and C# implementations.
The application stores only public verification keys, descriptions and lengths. Your secret phrase and the actual passwords are never written to disk. Passwords are recalculated whenever you need them, using the same deterministic algorithm.
Decentralized by design: no cloud, no database, no third-party trust required. Your secrets never leave your device.
Core Principles
- Zero-Storage Security - no passwords or secret phrases are ever stored or transmitted
- Decentralized Architecture - no central servers, no cloud dependency, no third-party trust
- Deterministic Regeneration - passwords are recreated identically from your secret phrase
- Metadata Only - only public keys, descriptions and lengths are stored
- Local Processing - all cryptographic operations happen on your device
- On-Demand Discovery - passwords exist only when you generate them
What you can do
- Add entries - register a service description and a secret phrase, choose a length, and store only the public verification key
- Get passwords - enter the secret phrase for an entry and regenerate the password on demand
- Verify secrets - prove knowledge of a secret phrase without exposing it or generating a password
- Edit metadata - change the description or the length at any time
- Delete entries - remove metadata when you no longer need it
- Copy to clipboard - one key press copies a generated password to the system clipboard
Key Features
- Decentralized & Serverless - no central database, no cloud lock-in
- No Password Database - eliminates password storage completely
- Deterministic Password Generation - same secret + same length = same password, always
- Public Key Verification - verify secret knowledge without exposure
- Full-Screen Terminal Interface - borders, colors, highlighted selection, modal forms
- Secure Input - hidden secret phrase entry with
Ctrl+Tshow/hide toggle - Real-Time Validation - live counters and validation of description, secret phrase and length
- Sliding Window Input - cursor stays visible while typing long secret phrases
- Copy to Clipboard - system clipboard on X11, Wayland, macOS, Windows; OSC 52 fallback including over SSH
- About Screen - version, author, license, repository and website
- Cross-Platform Data - same
passwords.jsonformat as Python, JS, Kotlin, Go and C# - No Network Access - runs entirely offline, no runtime dependencies
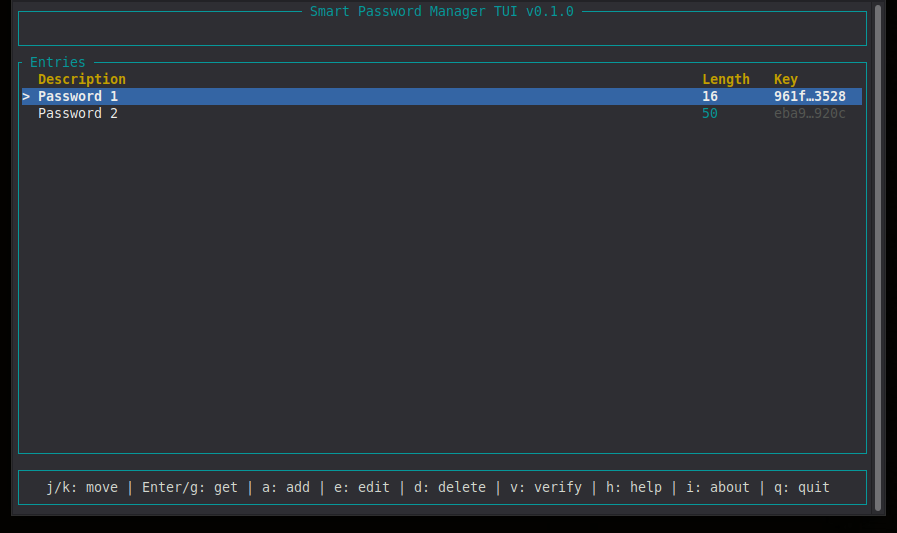
List screen
| Key | Action |
|---|---|
Up / k | Move selection up |
Down / j | Move selection down |
Enter / g | Get password for selected entry |
a | Add a new entry |
e | Edit selected entry (description and length) |
d | Delete selected entry (requires confirmation) |
v | Verify a secret phrase against selected entry |
h / ? | Open help |
i | Open About |
q / Esc | Quit |
Ctrl+C | Quit immediately |
Form screens
| Key | Action |
|---|---|
Tab | Next field |
Shift+Tab | Previous field |
Enter | Save / submit (only when the form is valid) |
Esc | Cancel and return to list |
Ctrl+T | Toggle secret phrase visibility |
Left | Move cursor left |
Right | Move cursor right |
Home | Jump to start of field |
End | Jump to end of field |
Backspace | Delete previous character |
Delete | Delete character under cursor |
Message screen
| Key | Action |
|---|---|
c | Copy payload to clipboard |
Enter / Esc / Space | Close message |
q | Quit |
Copy behavior
When you press c on a message that contains a password, the application tries two methods in order:
- System clipboard via the
arboardcrate. Works on X11, Wayland, macOS and Windows sessions. - OSC 52 escape sequence written to stdout. Works in most modern terminals and over SSH, because the sequence is interpreted by the terminal on the user's side.
If neither method is available, the message modal reports No clipboard available on this host, and the password can be selected manually from the screen.
smart-password-manager-tui --help
smart-password-manager-tui --version
With no arguments the application starts in interactive mode.
Creating Your First Entry
- Press
ato open the add form - Enter a service description (e.g.,
GitHub Account) - Enter your secret phrase (minimum 12 characters, never stored)
- Set password length (12–100 characters, 16–24 recommended)
- Press
Enter- only the public verification key is stored
Retrieving a Password
- Select an entry with
j/k - Press
gorEnter - Enter your secret phrase
- Password regenerates identically for copying
Editing Metadata
- Select an entry and press
e - Update the description or length
- Press
Enterto save
Deleting an Entry
- Select an entry and press
d - Confirm with
y- only metadata is removed
Verifying a Secret
- Select an entry and press
v - Enter your secret phrase
- The application reports whether the secret matches the stored public key - without generating or displaying the password
Only public keys, descriptions and lengths are stored, as JSON. The file location follows the standard user data directory convention for your operating system.
| Platform | Path |
|---|---|
| Linux | ~/.config/smart_password_manager/passwords.json |
| macOS | ~/.config/smart_password_manager/passwords.json |
| Windows | %USERPROFILE%\.config\smart_password_manager\passwords.json |
Format:
{
  "a3f8c1e0b9d2f4a6c8e0b1d3f5a7c9e1b2d4f6a8c0e2b4d6f8a0c2e4b6d8f0a1": {
    "public_key": "a3f8c1e0b9d2f4a6c8e0b1d3f5a7c9e1b2d4f6a8c0e2b4d6f8a0c2e4b6d8f0a1",
    "description": "GitHub Account",
    "length": 24
  }
}
What is NOT stored:
- Your secret phrase
- The actual password
- Any reversible password data
What IS stored:
- Public verification key (a hash derived from the secret)
- Service description
- Password length
The file is created automatically on first save. If it does not exist at startup, the application begins with an empty list.
Data Compatibility
- Uses the same
~/.config/smart_password_manager/passwords.jsonformat as the Python, JavaScript, Kotlin, Go and C# implementations - The same
smartpasslibalgorithm is used everywhere, so metadata can be synced through any channel without conversion - Consistent cryptographic operations across all ecosystem tools
Security Model
- Proof of knowledge - public keys verify secrets without exposing them
- Decentralized trust - no third party needed - you control your secrets completely
- Deterministic security - same secret + same length = same password, always
- Metadata separation - non-sensitive data stored separately from verification
- Local processing - no data leaves your computer
- No recovery backdoors - lost secret phrase = permanently lost access, by design
Decentralized Nature
There is no "forgot password" button. This is by design:
- No central server can reset your passwords
- No support team can recover your access
- Your secret phrase is the ONLY key
This is the price of true decentralization - you are completely in control.
Secret Phrase Security
Your secret phrase is the cryptographic master key
- Permanent data loss - lost secret phrase = irreversible loss of all derived passwords
- No recovery mechanisms - no password recovery, no secret reset, no administrative override
- Deterministic generation - identical input (secret + length) = identical output (password)
- Single point of failure - secret phrase is the sole authentication factor for all passwords
- Secure storage required - digital storage of secret phrases is prohibited
Critical: Test password regeneration with non-essential accounts before production use.
Secret Phrase Requirements
- Minimum 12 characters (enforced by the application)
- Case-sensitive -
MySecretandmysecretare different - Use a mix of: uppercase, lowercase, numbers, symbols, emoji, or Cyrillic
- Never store digitally
- NEVER use your password description as your secret phrase
Strong Secret Examples
" ! MyStrongSecretPhrase2026"   - mixed case + numbers + symbols
"P@ssw0rd!LongSecret"           - special chars + numbers + length
"КотБегемот2026НаДиете"         - Cyrillic + numbers
"Correct-Horse-Battery-42"      - memorable phrase with separator
Weak Secret Examples (avoid)
"short"                  - too short, rejected
"GitHub Account"         - using description as secret (weak!)
"password"               - dictionary word, too short
"1234567890"             - only digits, too short
"qwerty123"              - keyboard pattern
Same as description      - never use the same value as description
Powered by smartpasslib - the core library for deterministic password generation.
Key derivation
| Key Type | Iterations | Purpose |
|---|---|---|
| Private Key | 15–30 (dynamic) | Password generation (never stored, never transmitted) |
| Public Key | 45–60 (dynamic) | Verification (stored locally) |
Character set (Google-compatible)
!@#$%^&*()_+-=[]{};:,.<>?/ABCDEFGHIJKLMNOPQRSTUVWXYZ0123456789abcdefghijklmnopqrstuvwxyz
Validation rules
- Secret phrase: minimum 12 characters
- Password length: 12–100 characters
Decentralized architecture
- No central authority required
- Metadata can be synced via any channel
- Your security depends only on your secret phrase
- Works offline - no internet connection required
The same deterministic algorithm is available in multiple languages. Smart Password Manager TUI produces identical passwords to:
| Language | Repository |
|---|---|
| Python | smartpasslib |
| JavaScript | smartpasslib-js |
| Kotlin | smartpasslib-kotlin |
| Go | smartpasslib-go |
| C# | smartpasslib-csharp |
| Rust | smartpasslib-rs |
Data transfer: Metadata can be moved between platforms through the shared passwords.json format.
From crates.io
cargo install smart-password-manager-tui
Prebuilt binary (Linux, static musl)
Download from the Releases page:
chmod +x smart-password-manager-tui-<version>-linux-x86_64-musl
./smart-password-manager-tui-<version>-linux-x86_64-musl
From source
Requires Rust 1.88 or newer (edition 2024).
git clone https://github.com/smartlegionlab/smart-password-manager-tui-rs.git
cd smart-password-manager-tui-rs
cargo build --release
./target/release/smart-password-manager-tui
Build and install to your home directory
cargo build --release
install -Dm755 target/release/smart-password-manager-tui ~/.local/bin/smart-password-manager-tui
One-command install
curl -fsSL https://raw.githubusercontent.com/smartlegionlab/smart-password-manager-tui-rs/master/install.sh | bash
Uninstall
rm -f ~/.local/bin/smart-password-manager-tui
Your password metadata in ~/.config/smart_password_manager/passwords.json is never touched by the uninstaller. Delete it manually if you want to remove it:
rm -rf ~/.config/smart_password_manager
Termux (Android)
After cargo install, Termux won't find the binary because ~/.cargo/bin is not in PATH. Add it once:
echo 'export PATH="$HOME/.cargo/bin:$PATH"' >> ~/.bashrc
source ~/.bashrc
smart-password-manager-tui-rs/
├── Cargo.toml
├── Cargo.lock
├── .gitignore
├── LICENSE
├── README.md
├── install.sh
├── uninstall.sh
└── src/
    ├── main.rs        Entry point, terminal setup, event loop, CLI parsing
    ├── app.rs         Application state, screen enum, event handling
    ├── input.rs       Plain and password input widgets with cursor
    ├── ui.rs          Top-level render dispatcher
    └── screen/
        ├── mod.rs
        ├── list.rs    Table of stored entries
        ├── form.rs    Add / Edit / Get / Verify forms
        ├── confirm.rs Delete confirmation dialog
        ├── message.rs Success and error messages
        ├── help.rs    Full key binding reference
        └── about.rs   Version, author, license and links
- Pointer-Based Security Paradigm - Architectural Shift from Data Protection to Data Non-Existence
- Local Data Regeneration Paradigm - Ontological Shift from Data Transmission to Synchronous State Discovery
Core Libraries
- smartpasslib - Python
- smartpasslib-js - JavaScript
- smartpasslib-kotlin - Kotlin
- smartpasslib-go - Go
- smartpasslib-csharp - C#
- smartpasslib-rs - Rust
CLI Applications
- CLI Smart Password Manager (Python)
- CLI Smart Password Generator (Python)
- CLI Smart Password Manager (C#)
- CLI Smart Password Generator (C#)
- CLI Smart Password Manager (Rust)
Desktop Applications
- Desktop Smart Password Manager (Python)
- Desktop Smart Password Manager (C#)
- Desktop Smart Password Manager (Rust, GUI)
- Desktop Smart Password Manager (Rust, TUI) - this project
Other
By using this software, you agree to the full disclaimer terms.
Software provided "AS IS" without warranty. You assume all risks.
Full legal disclaimer: See DISCLAIMER.md
License: BSD 3-Clause License